On July 25, we hacked OpenAI.
Two bugs let us take over ChatGPT/Codex accounts of OpenAI employees (+some unaffiliated users) and reach connected services: Outlook, Slack, GitHub, etc.
We proved it with a PR in OpenAI’s internal codebase . It took us <72h. 🧵
s1r1us
@S1r1u5_
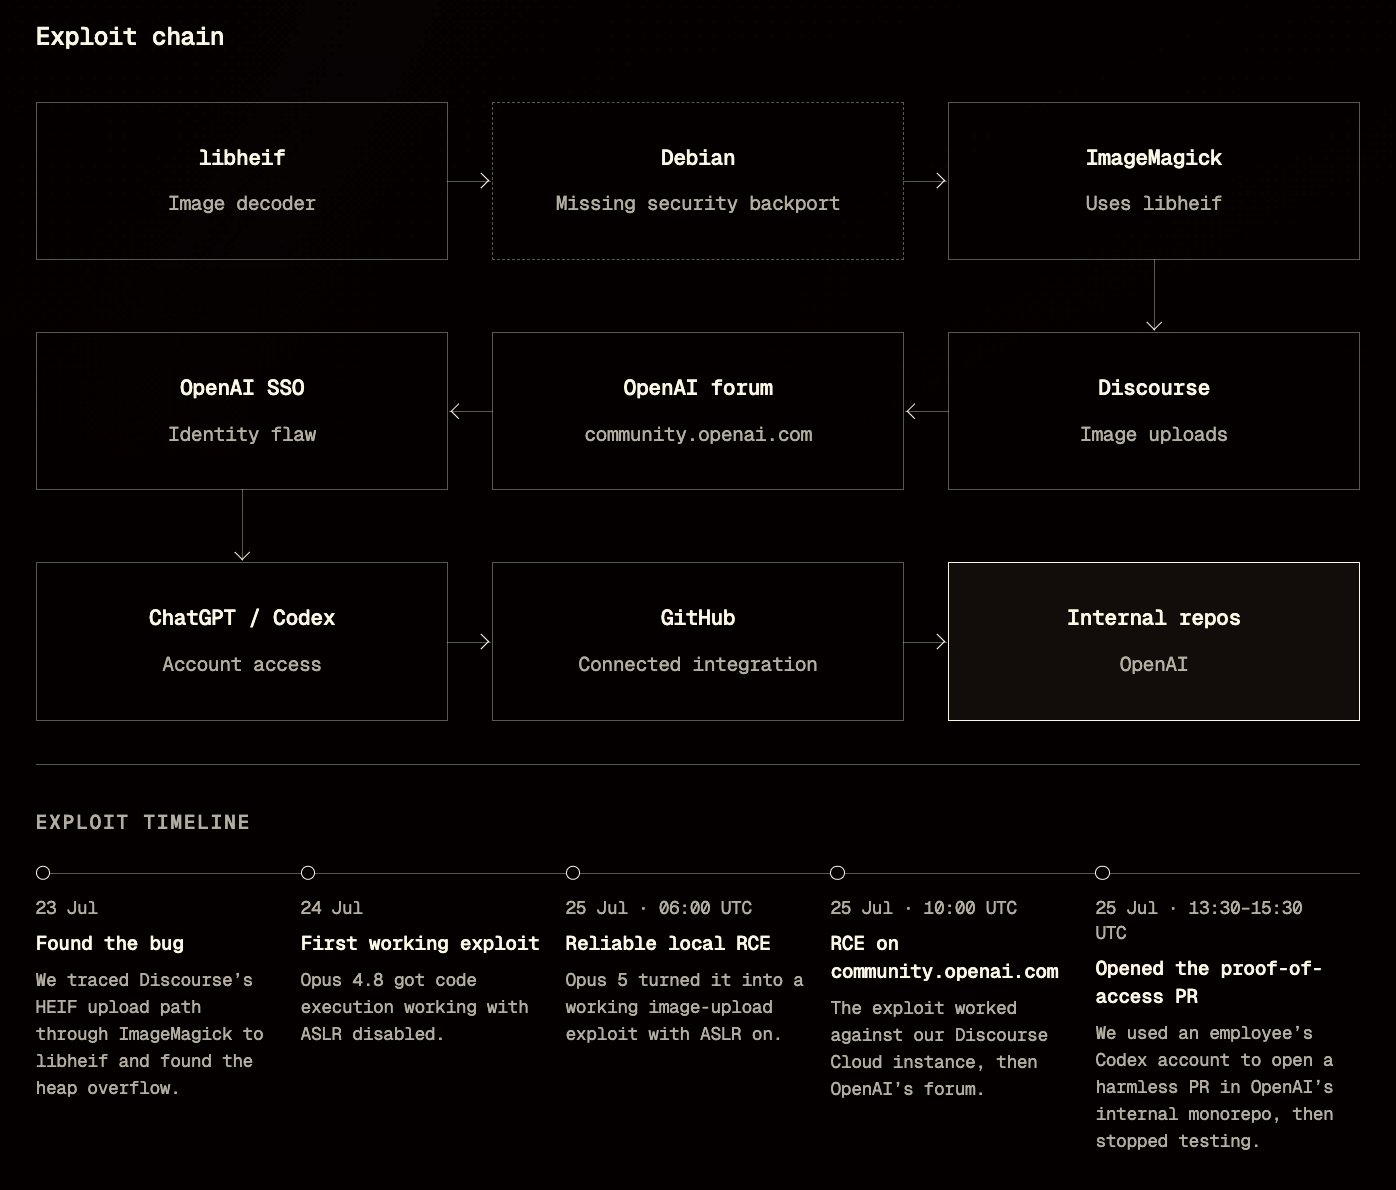
At a high level, this was the full exploit chain.
1. HEIC/HEIF upload
2. ImageMagick decoding
3. Heap overflow on libheif
4. RCE on community.openai.com
5. Critical OpenAI SSO flaw
6. ChatGPT/Codex takeover
7. Connected GitHub access
8. Internal repo PR #1186742
1. HEIC/HEIF upload
2. ImageMagick decoding
3. Heap overflow on libheif
4. RCE on community.openai.com
5. Critical OpenAI SSO flaw
6. ChatGPT/Codex takeover
7. Connected GitHub access
8. Internal repo PR #1186742
2:43 AM UTC · Sep 18, 2026 · 223.7K Views
15611.4K411
s1r1us
@S1r1u5_
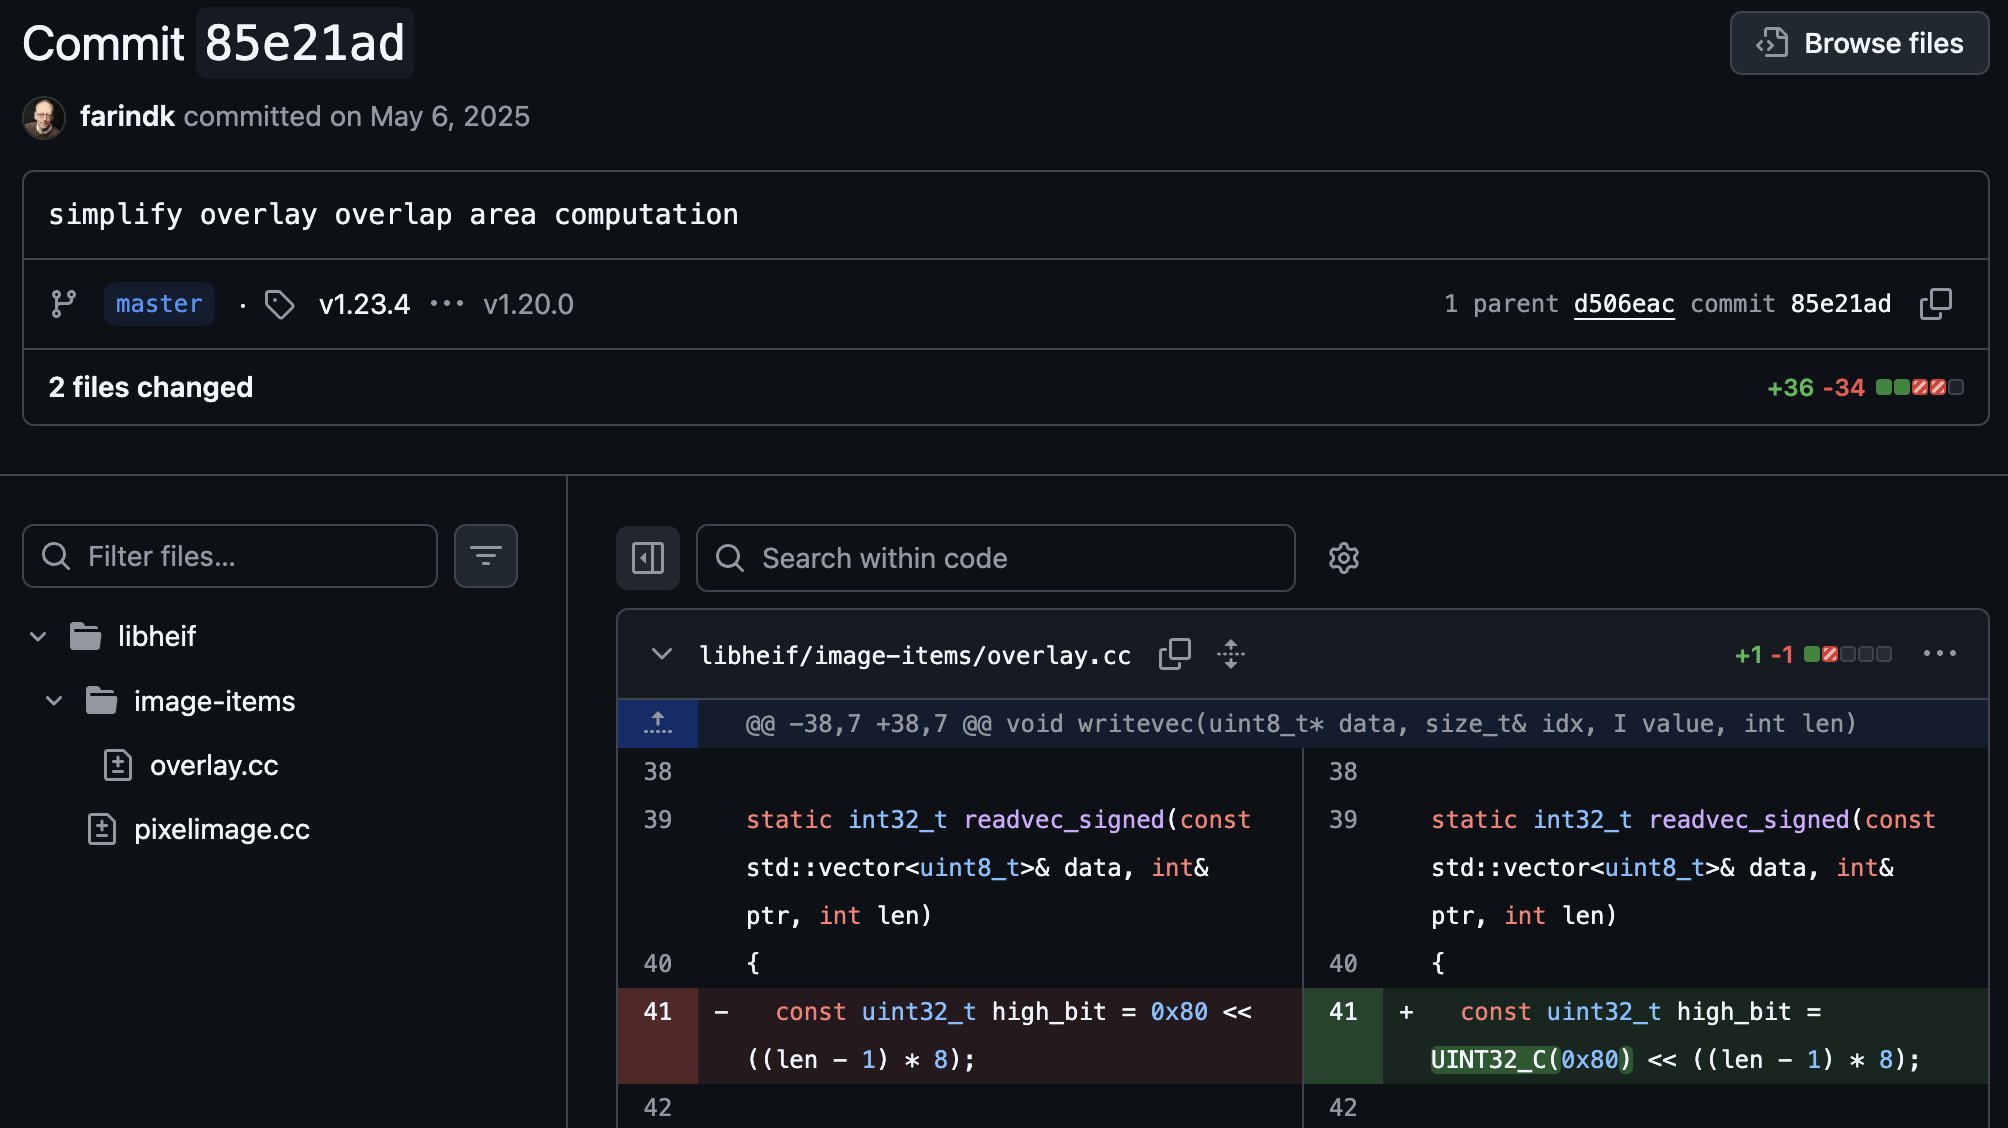
The image package libheif had a known vulnerability, fixed upstream, but the fix never flagged as security-relevant and was still present in Discourse. Uploading a HEIF file gave us RCE on the OpenAI forum community.openai.com.
github.com/strukturag/lib…
github.com/strukturag/lib…
2:43 AM UTC · Sep 18, 2026 · 148.3K Views
81666385
s1r1us
@S1r1u5_
The second bug is more serious: an OpenAI SSO vulnerability.
Using this flaw, we turned our Discourse forum exploit into access to ChatGPT and Codex accounts belonging to people who had signed into it, including OpenAI employees.
Using this flaw, we turned our Discourse forum exploit into access to ChatGPT and Codex accounts belonging to people who had signed into it, including OpenAI employees.
2:43 AM UTC · Sep 18, 2026 · 123.6K Views
21358538
s1r1us
@S1r1u5_
Those accounts could be (and some were) connected to Outlook, Gmail, Google Drive, Slack, GitHub, and other services via Codex or ChatGPT. This made the potential impact much larger than ChatGPT alone.
2:43 AM UTC · Sep 18, 2026 · 120K Views
21247428
s1r1us
@S1r1u5_
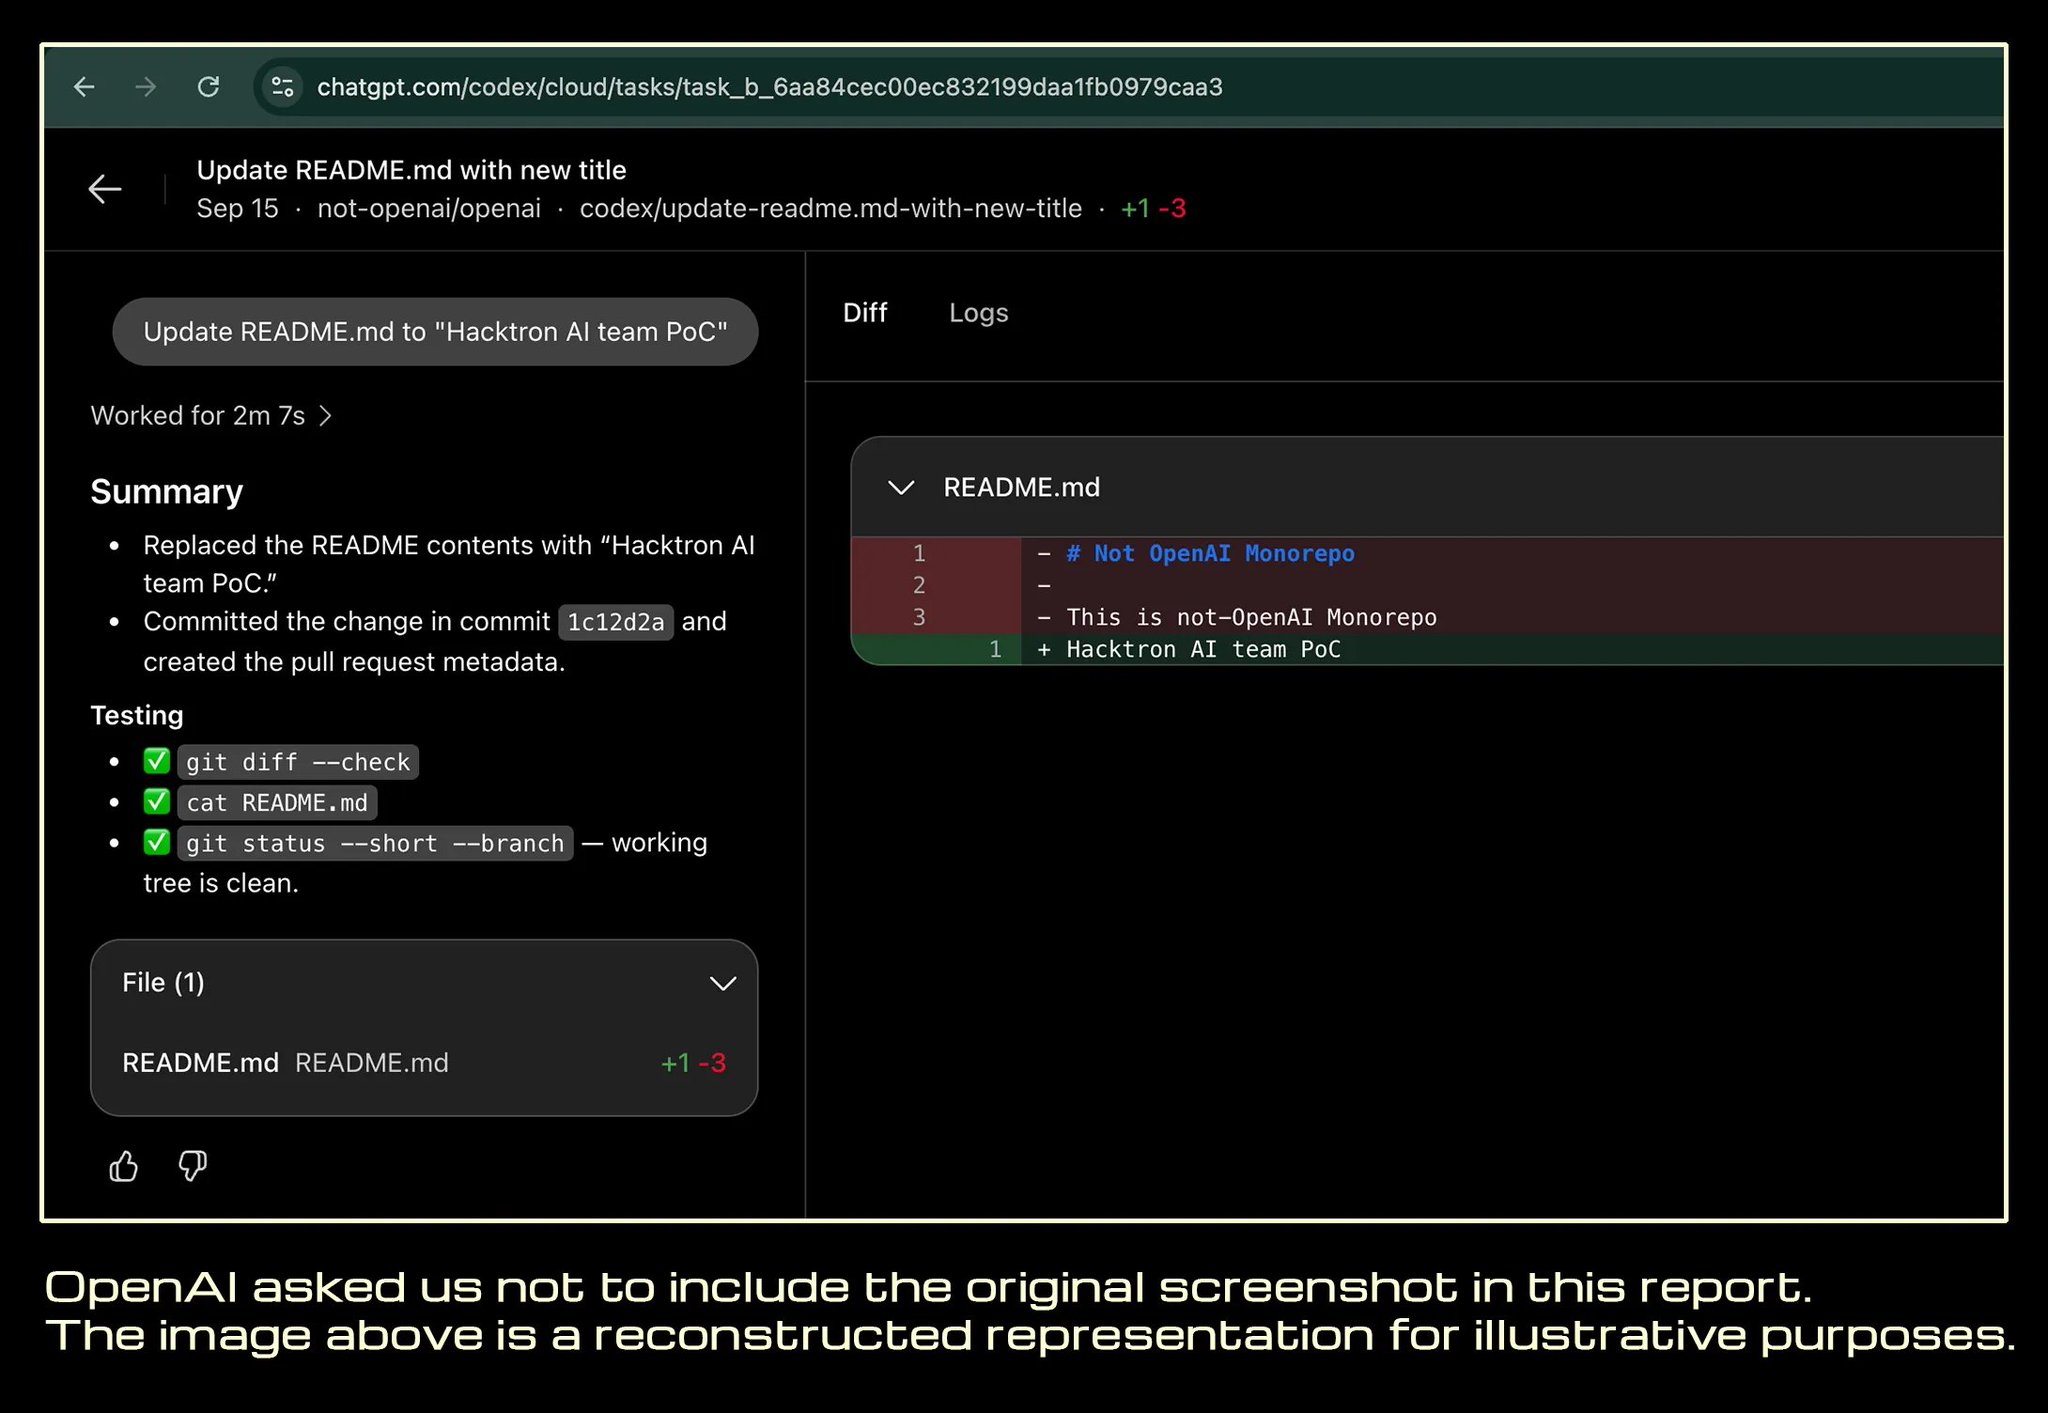
To demonstrate impact while minimising exposure, we used one affected employee account connected to OpenAI’s GitHub org.
Codex created a harmless PR in their internal monorepo without us reading sensitive code. That proved to us that the access was real.
Codex created a harmless PR in their internal monorepo without us reading sensitive code. That proved to us that the access was real.
2:43 AM UTC · Sep 18, 2026 · 122.3K Views
31149424
s1r1us
@S1r1u5_
We reported the bug to Discourse and OpenAI. OpenAI fixed the SSO issue roughly 14 hours after our initial submission.
Discourse received our separate report Saturday, replied Sunday, and had a fix Monday.
OpenAI awarded us $6,500.
Discourse received our separate report Saturday, replied Sunday, and had a fix Monday.
OpenAI awarded us $6,500.
2:43 AM UTC · Sep 18, 2026 · 528.3K Views
70441.1K129
s1r1us
@S1r1u5_
AI agents did a meaningful share of the exploit work.
Opus 4.8 found the libheif vulnerability and built a partial exploit. Hours after Opus 5 launched, it adapted the exploit to Discourse and achieved RCE on our test instance.
Opus 4.8 found the libheif vulnerability and built a partial exploit. Hours after Opus 5 launched, it adapted the exploit to Discourse and achieved RCE on our test instance.
2:43 AM UTC · Sep 18, 2026 · 105.3K Views
51357233
s1r1us
@S1r1u5_
Our main takeaway from hacking OpenAI: AI is reducing the amount of scarce expertise needed to develop exploits. Work that once took months can now take days.
Even leading AI labs can be vulnerable.
Defenders need to fix the architecture, patch faster, and limit the blast radius of connected things.
Even leading AI labs can be vulnerable.
Defenders need to fix the architecture, patch faster, and limit the blast radius of connected things.
2:44 AM UTC · Sep 18, 2026 · 100.1K Views
95574557
s1r1us
@S1r1u5_
This work was done by our team @HacktronAI led by @rootxharsh along with me and @iamnoooob.
We have published the full details of the exploit chain, as well as how we discovered it, on our blog here:
hacktron.ai/blog/hacking-o…
We have published the full details of the exploit chain, as well as how we discovered it, on our blog here:
hacktron.ai/blog/hacking-o…
hacktron.ai
Hacking OpenAI
A heap overflow and SSO misconfiguration to compromise OpenAI internal repositories
2:44 AM UTC · Sep 18, 2026 · 100.4K Views
1062696192
s1r1us
@S1r1u5_
also we are not some random dudes, check our work before, we work with companies like perplexity and vercel.
hacktron.ai/blog/
hacktron.ai/blog/
hacktron.ai
Blog | Hacktron AI
Hacktron autonomously reviews code, finds vulnerabilities, and writes exploits.
3:35 AM UTC · Sep 18, 2026 · 95.7K Views
71454052